Teams external sharing reviews: 6 ways to enable secure collaboration outside of your organization


Microsoft Teams migration guide
Discover how to simplify the migration process from planning to post-migration management!
Learn More
Master Hacks: Migrate like a pro
Check out our video series to help you turn migration projects into masterpieces!
Table of contents
TL;DR: Digital collaboration with external organizations is part of everyday business, especially with remote work. Get visibility into your teams' external access practices and control Microsoft Teams' external users securely with these step-by-step best practices (with pictures).
Should those budget spreadsheets still be shared with your organization’s former accounting firm? Who still has access to last quarter’s user research reports?
These kinds of questions were constantly coming up within the ShareGate team—and became an essential part of planning our Microsoft 365 governance solution.
Teams tips: Learn Microsoft Teams governance best practices for secure collaboration
In this article we’ll walk through six ways to see who outside your organization has access to your teams, what each one shows you, what each one misses, and what it costs.
4 ways someone outside of your organization can end up in your Microsoft 365 environment
1. Guest access: The classic one! Someone added to a team as a member. They get an Entra B2B guest object in your directory, so they show up everywhere you’d expect: the Teams admin center Guests column, the Microsoft 365 admin center guest list, Entra, the audit log, and access reviews. On by default.
2. External access (federation): Chat and meetings with another organization. No account is created—they stay in their own tenant so they don't appear on a guest list. They also can’t reach your teams, channels or files, so there’s less to review. On by default.
3. Shared channels (B2B direct connect): Someone invited into a single channel of a team. They have no presence in your directory at all and don't appear on a guest list. This is the blind spot, and we come back to it below. Off by default.
4. Anonymous meeting join: No account, no record. Microsoft is explicit that an anonymous participant’s identity can’t be verified before, during or after the meeting. On by default.
Why are external access reviews important to do regularly?
Microsoft Teams enables you to collaborate internally and with business users from external organizations—such as clients, vendors, or partners.
Depending on your settings, business users can invite anyone with an email address into a team as a guest, where they can reach the team’s conversations, files and resources. Team owners can also invite people from other organizations into a single shared channel, that works a bit differently. More on that soon.
But the convenience of self-service has led to a need for better access management capabilities. Consider the following:
- When someone at a supplier or agency leaves their job, nothing in your tenant changes. How long do their credentials keep working in your teams?
- If a file was shared with an individual outside your organization rather than with a team, would it show up in any review?
- When a project with an external partner wraps up, who removes their access and how would you know it hadn’t happened?
While too many restrictions can hurt user adoption, excessive access rights are equally undesirable. The latter situation indicates a lack of control over access and can lead to audit findings and compromises.
As an IT admin, you need to proactively talk with team owners to make sure they review who has access to their resources. In other words, you need to be conducting regular access reviews.
Option #1: Verify external guest user access directly in Microsoft Teams
Depending on how your SharePoint sharing settings are configured, guest users in Teams likely have access to their team’s shared documents. So reviewing a list of your guest users can help give you some idea of what’s been shared with whom.
See your guest users: Microsoft Teams admin center
The Teams Administrator, can view all of your teams guest users in the Microsoft Teams admin center (Teams > Manage teams).
Do you only need to look rather than change anything? The Teams Reader role is sufficient.
From there, you can see a list of all your teams along with the number of guests each one has:
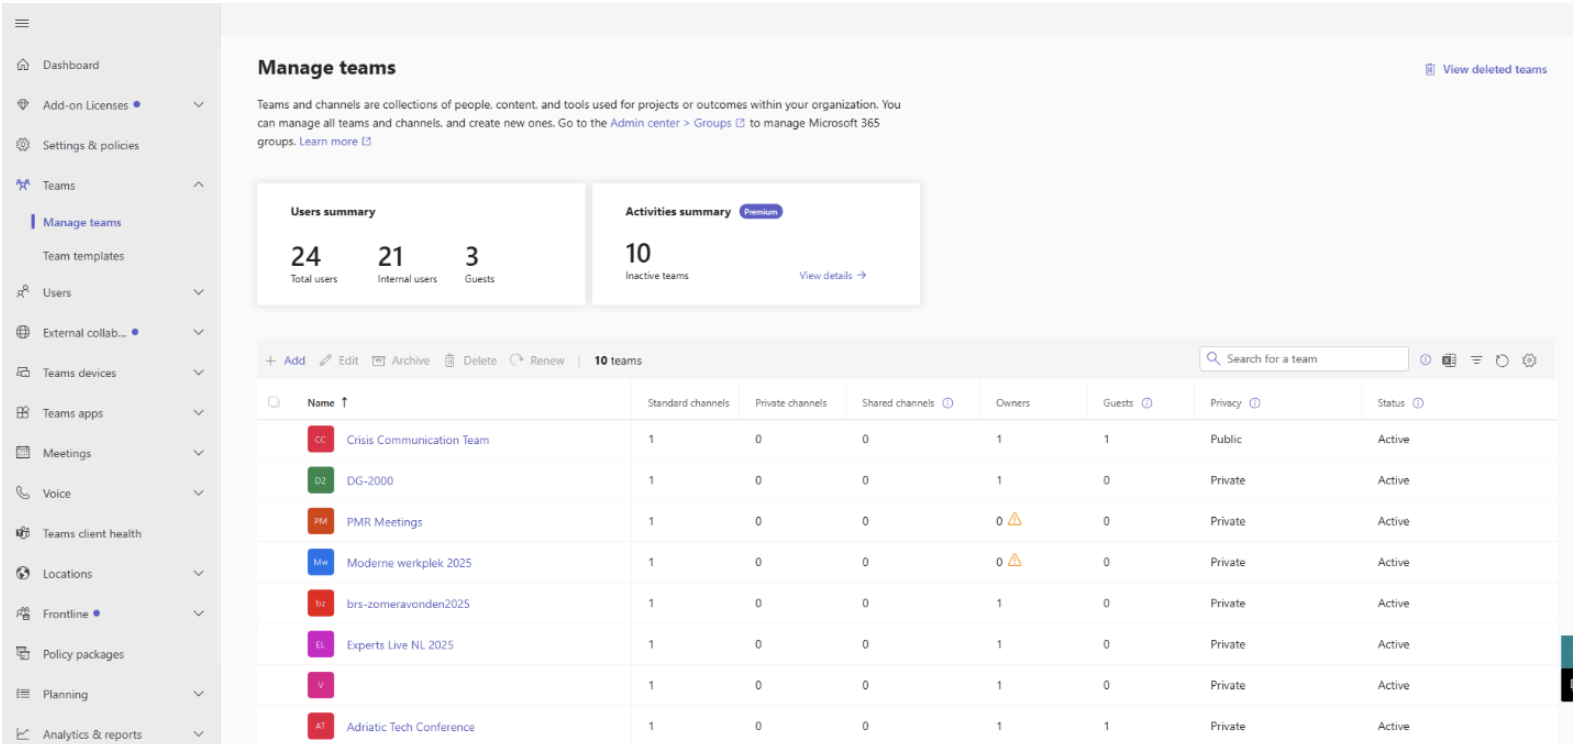
Microsoft defines it as “a count of Microsoft Entra B2B guests who are members of this team,” which is worth holding onto for later.
The grid has a few new columns, such as shared channels, and Sensitivity and Expiration date. Plus, columns are now toggleable via Edit columns, so you may need to switch Guests on before you see it.
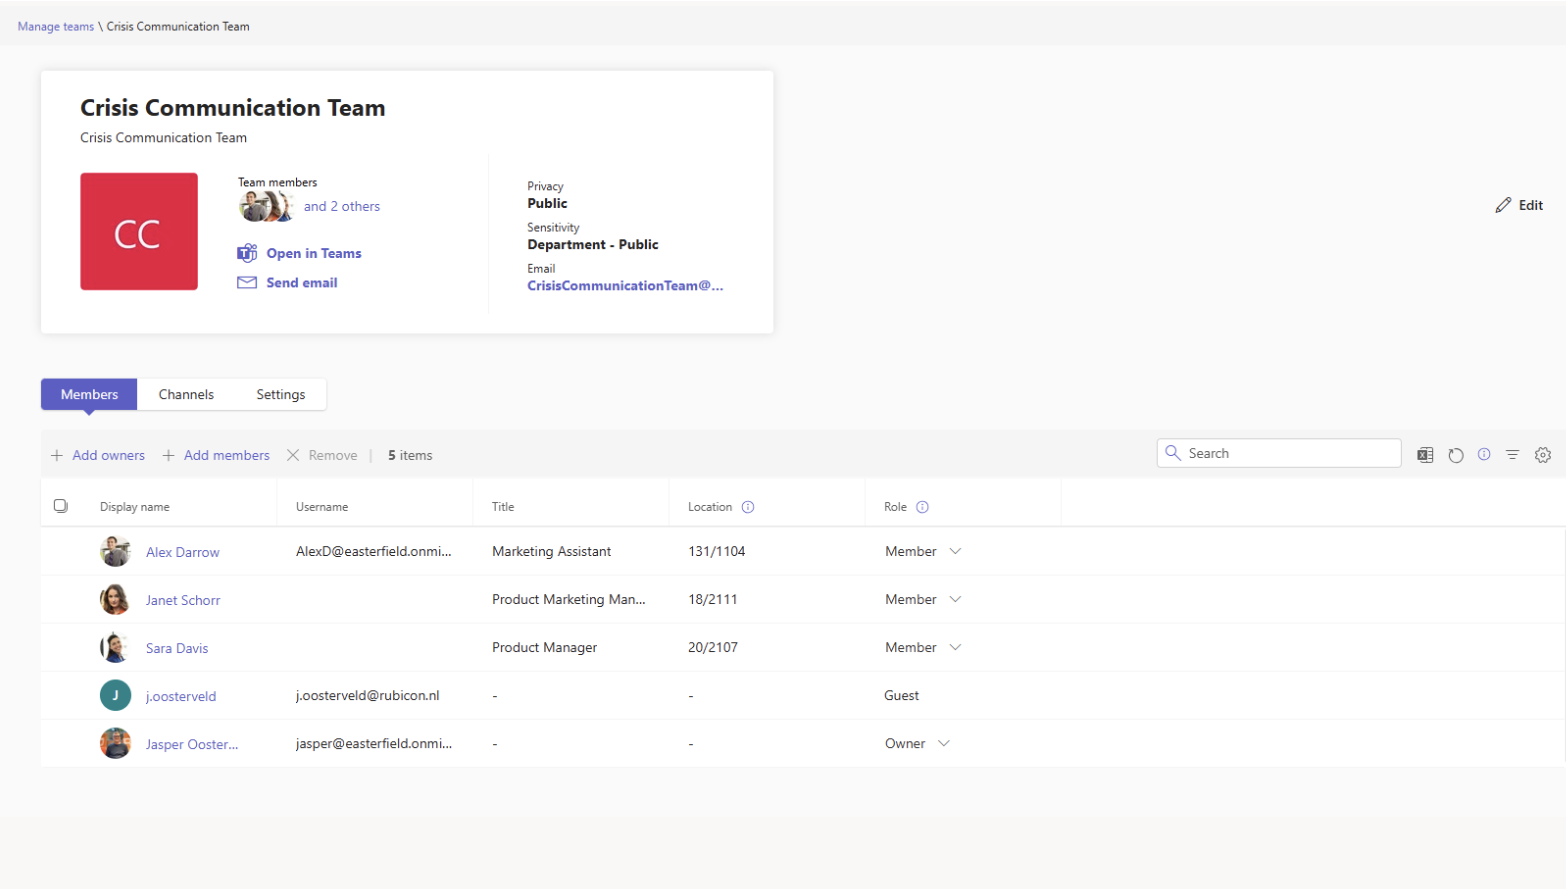
Then, click an individual team to open its team profile page. It'll show membership details, such as members, owners and guests, including the team channels and settings. Each channel has its own profile page too, which is where shared channel membership is accessible.
See a team's guest users: Microsoft Teams app
Since owners know who their team needs to collaborate with regularly, they're the ones who can validate guest access.
You can either send owners a list of their team’s guest users to review—or ask them to check guest membership for themselves in the Teams app by selecting More options next to their team name > Manage team > Members.
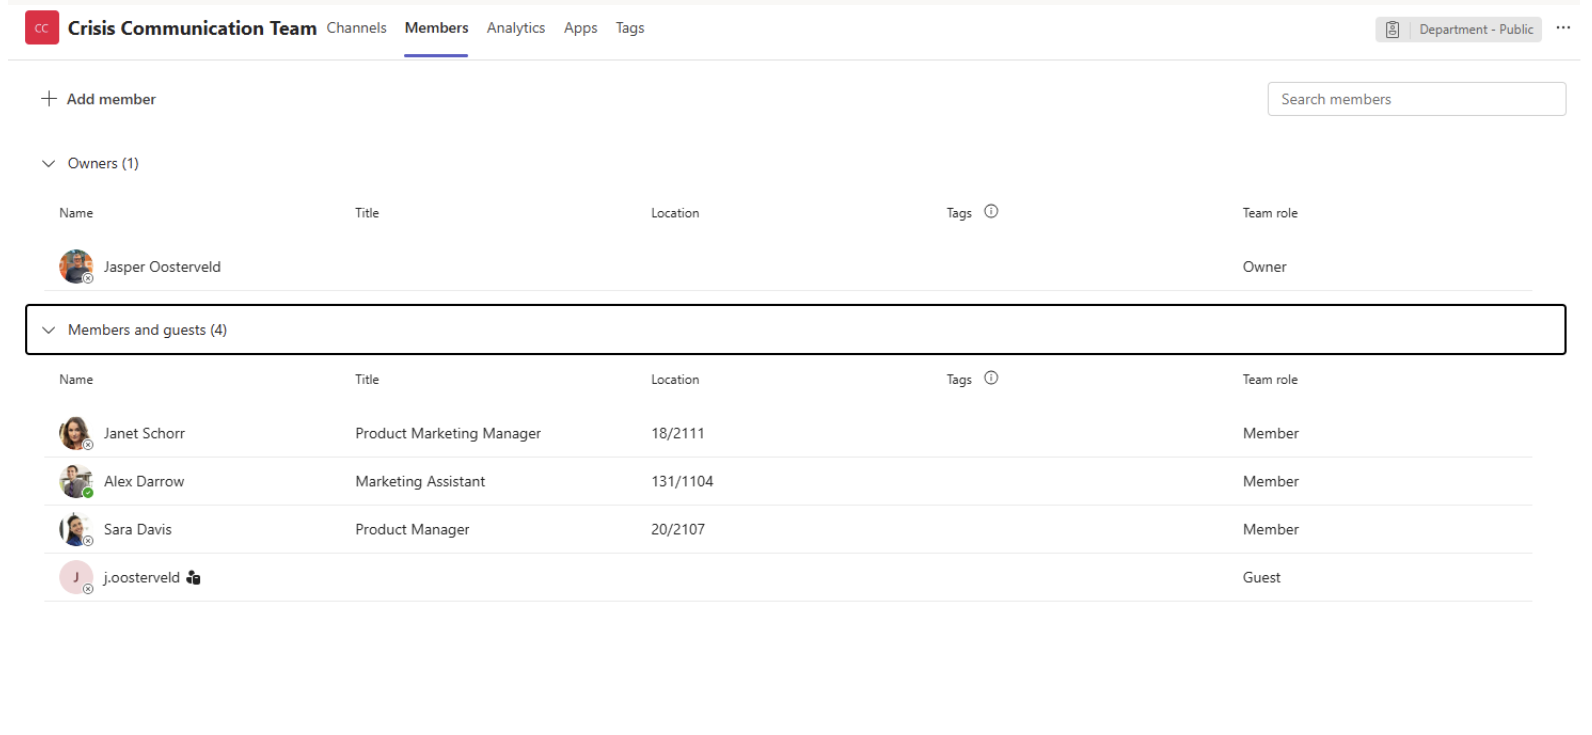
Any guests that shouldn’t have (or no longer need) access to their team can be deleted in the same interface in Teams.
You’ll probably need to follow up with various owners to make sure they’ve actually reviewed membership.
Then, you still have to log any changes they make for audit and compliance purposes. After all of that is finally said and done, you’ll be just about ready to start on the next review; for ongoing security, you need to review guest access regularly.
This option still requires a lot of work, and it still only shows you people who were added to the team. Someone with a link to one file in the team’s SharePoint site isn’t a team member and won’t appear here.
What has changed is where those people do show up. External sharing in SharePoint and OneDrive is moving from SharePoint’s own one-time-passcode authentication to Microsoft Entra B2B, which means authenticated external sharing now creates a guest account in your directory. The person your colleague shared a budget spreadsheet with will appear in your tenant-wide guest list. Just not in this teams overview.
The exception, and it’s an important one: Anyone links are unaffected. They create no identity at all, so no guest-based review will ever find them. That’s why we advise against using that sharing link.
Mark your calendar
Microsoft is moving all tenants to Entra B2B for external sharing. No opt-out. This hits every Microsoft 365 tenant.
- You can enable the integration manually until the end of April 2026. After that, you're on Microsoft's rollout schedule with no say in the date.
- From July 2026, external collaborators without a Microsoft Entra B2B guest account in your directory will see access denied.
- Previously shared links still work — as long as the recipient has a B2B guest account.
- If a guest account already exists, Microsoft won't create a duplicate.
Run the sharing report in Option #2 below and check the User email column. That's Microsoft's own recommended way to find guests who were invited via the old one-time-passcode flow and don't yet have a B2B account. Create those accounts now, before anyone loses access in July.
Shared channels
Shared channels let a team owner invite people from another organization into a single channel without adding them to the team. They use Entra B2B direct connect, and Microsoft is explicit about what that means for your directory:
"B2B direct connect users don't have a presence in your Microsoft Entra organization, so these users are managed in the Teams client by the shared channel owner."
Microsoft also makes clear that guests, including those converted to members, can't be added to a shared channel.
The practical consequence: a team whose entire external collaboration happens in a shared channel shows 0 in the Guests column, nothing in Manage team > Members, and nothing in the sharing report.
Where guest users actually show up
Four places to look:
1. Teams admin center—reports shared channels and external B2B direct connect members per team
2. Teams audit logs—covers shared channel lifecycle and cross-tenant member add, remove, promote, and demote
3. Entra access reviews—can detect them, with two exceptions: they're excluded from reviews scoped to "All Microsoft 365 groups with guest users," and they only appear in single-stage reviews
4. SharePoint site permissions report the External participant permissions column counts exactly these users
One important gap
An access review can detect individual external users in a shared channel, but not another entire team that's been shared into the channel. Only the channel owner can see and remove those, from inside Teams.
Good news: shared channels are off by default and require cross-tenant trust configured on both sides. That said, any tenant that switched it on made a deliberate decision and almost certainly hasn't revisited their review process since.
Option #2: Manually review external sharing links for each team's SharePoint site
To make sure you catch all external sharing links, including those shared with external users who aren’t team guests, it's possible to generate a report on file and folder sharing in each team’s associated SharePoint site.
Report on externally shared files and folders for each SharePoint site
Running a file and folder-sharing report on a given SharePoint site can help you understand how sharing is being used within the associated team.
The CSV report will tell you whether files or folders are shared with guests. It'll have a row for every unique file, user, permission and link on that site.
Columns cover the resource path, item type, permission level, user name and email, user or group type, link ID and link type including AccessViaLinkID, which tells you which sharing link someone used to reach an item.
Two limitations matter here:
1. “The report doesn’t include links that are emailed directly but aren’t clicked, or Anyone links,” and;
2. “The report shows SharePoint groups, but not individual users inside them.”
What does this mean? A link sitting unclicked in someone’s inbox is invisible, an Anyone link is invisible, and a SharePoint group with fifteen people in it shows up as one row.
To run the sharing report for a SharePoint site:
1. Navigate to the team’s associated SharePoint site where you want to run a report.
2. Click on the site’s Settings menu, then select Site usage.
Scroll down to the Shared with external users section and click Run report.
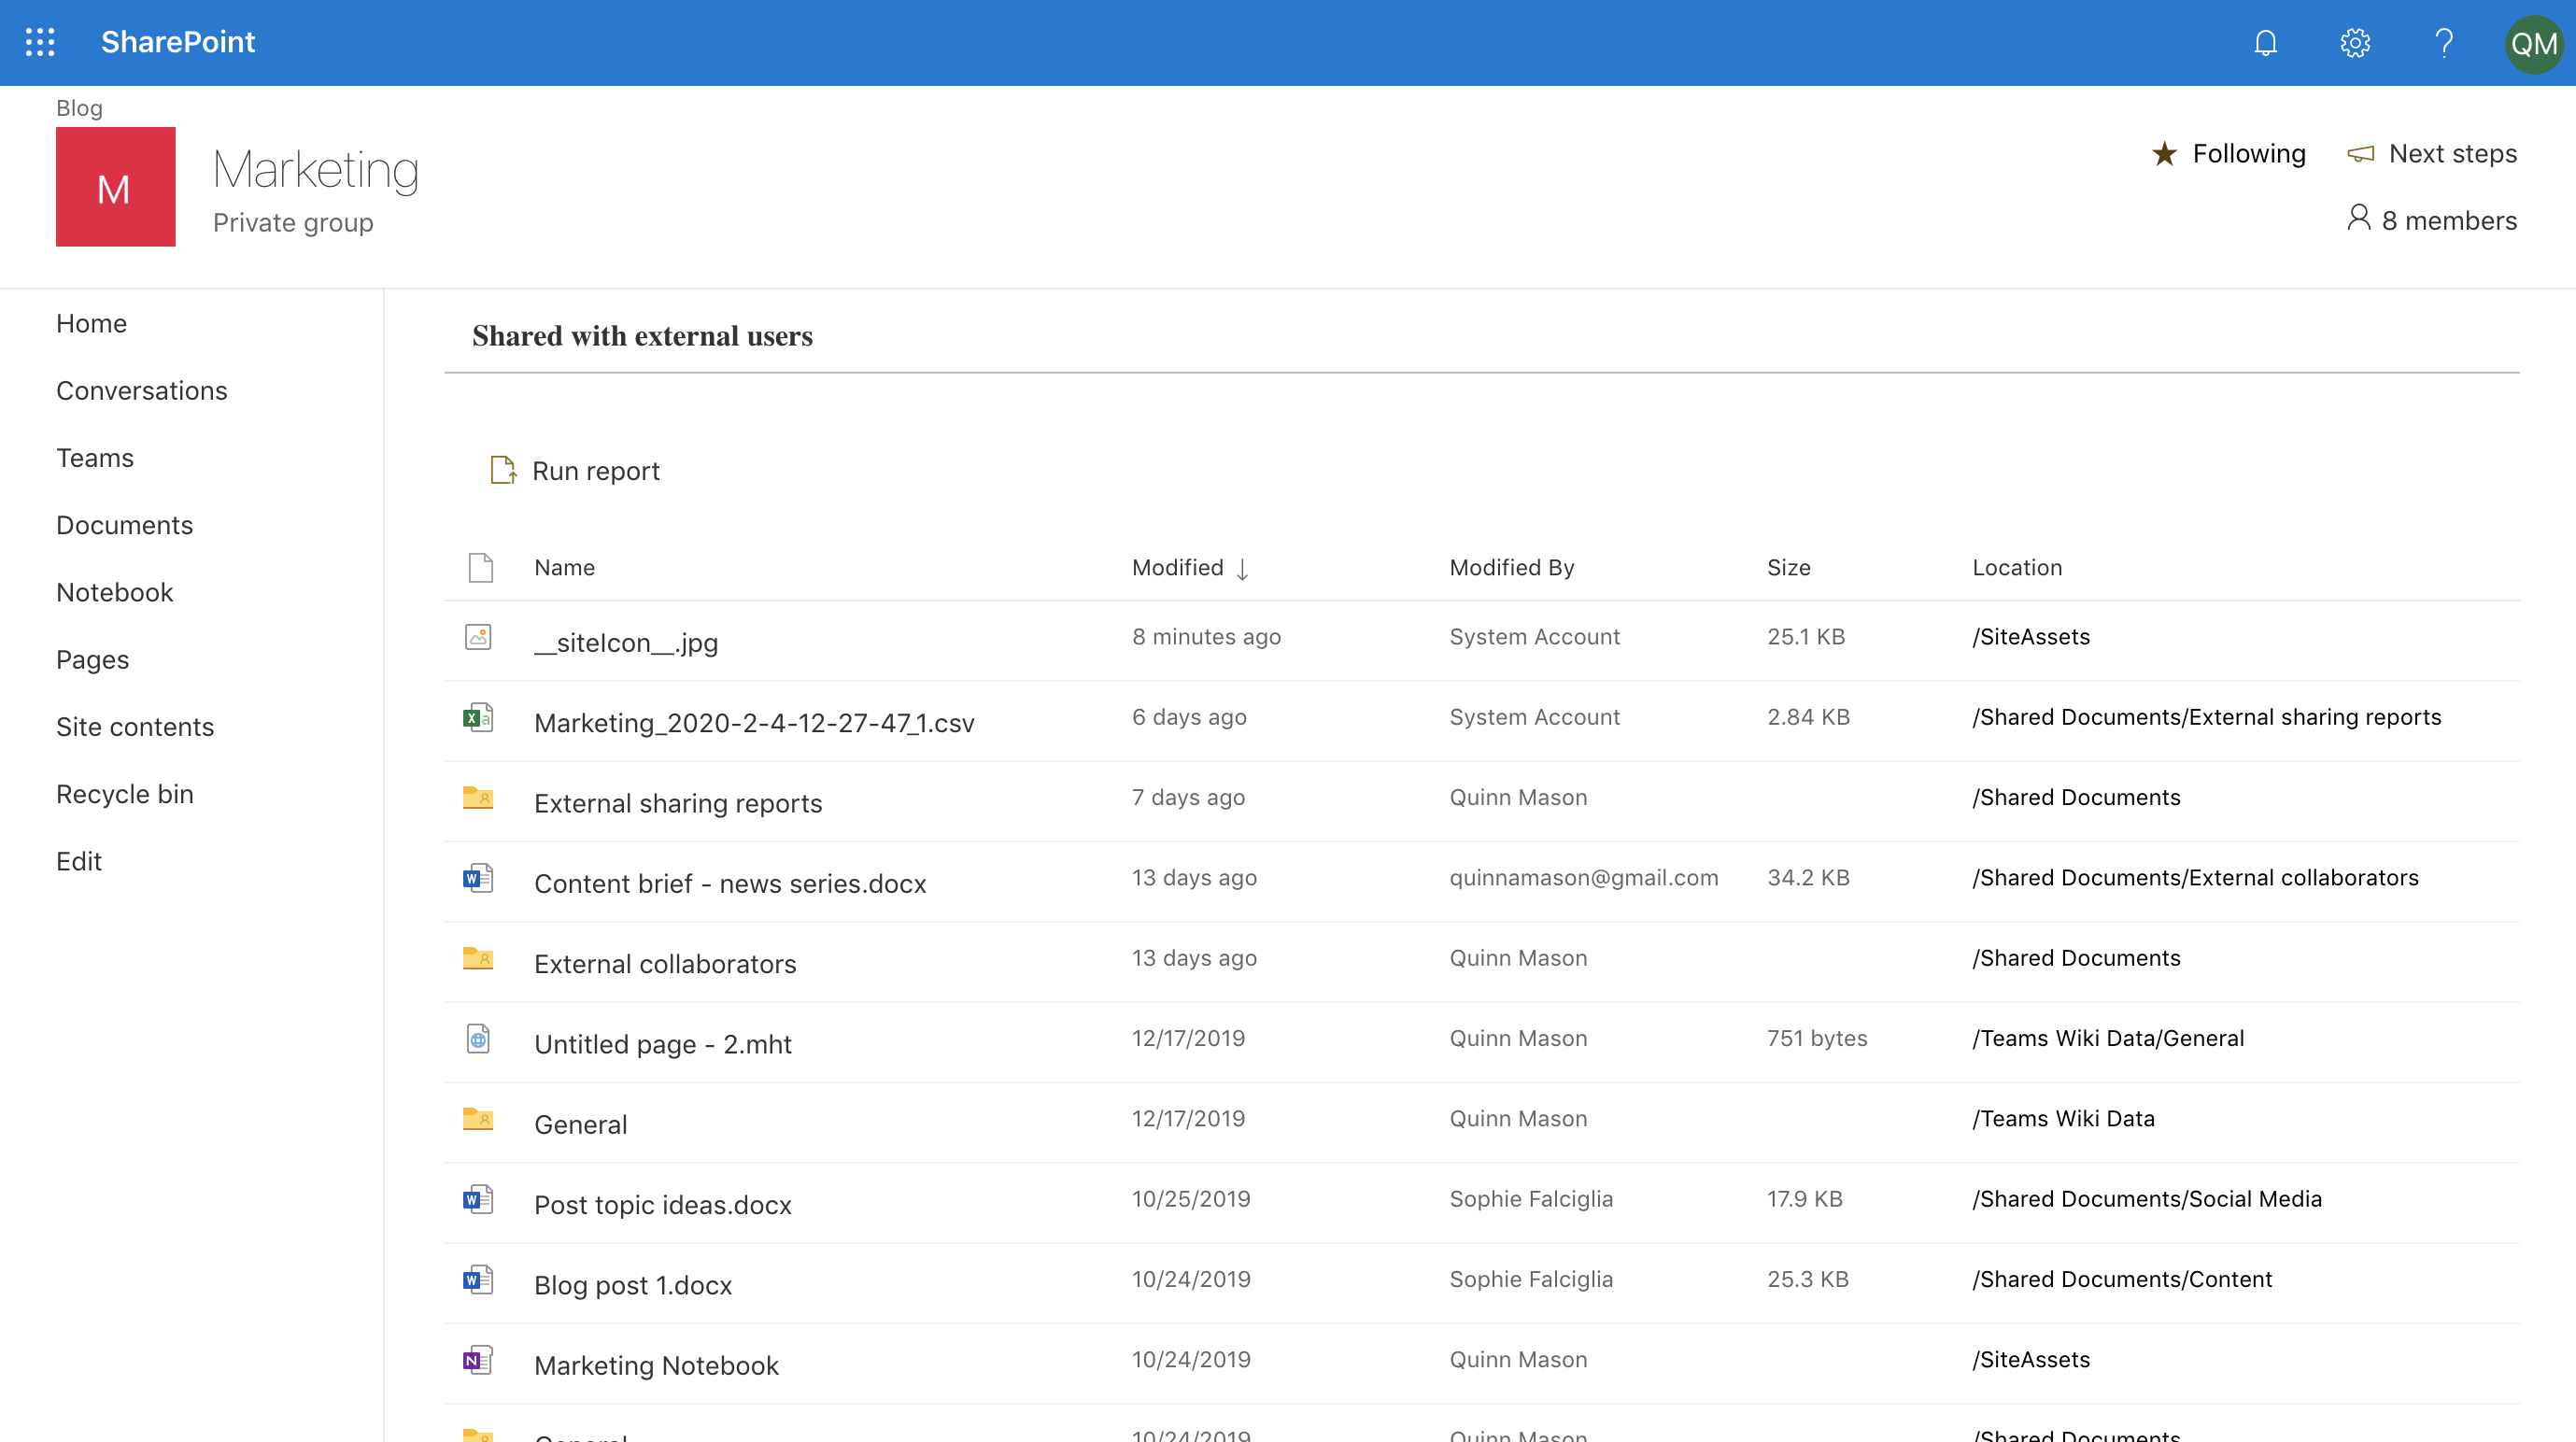
Choose the location where you want to save the report, then click Save.
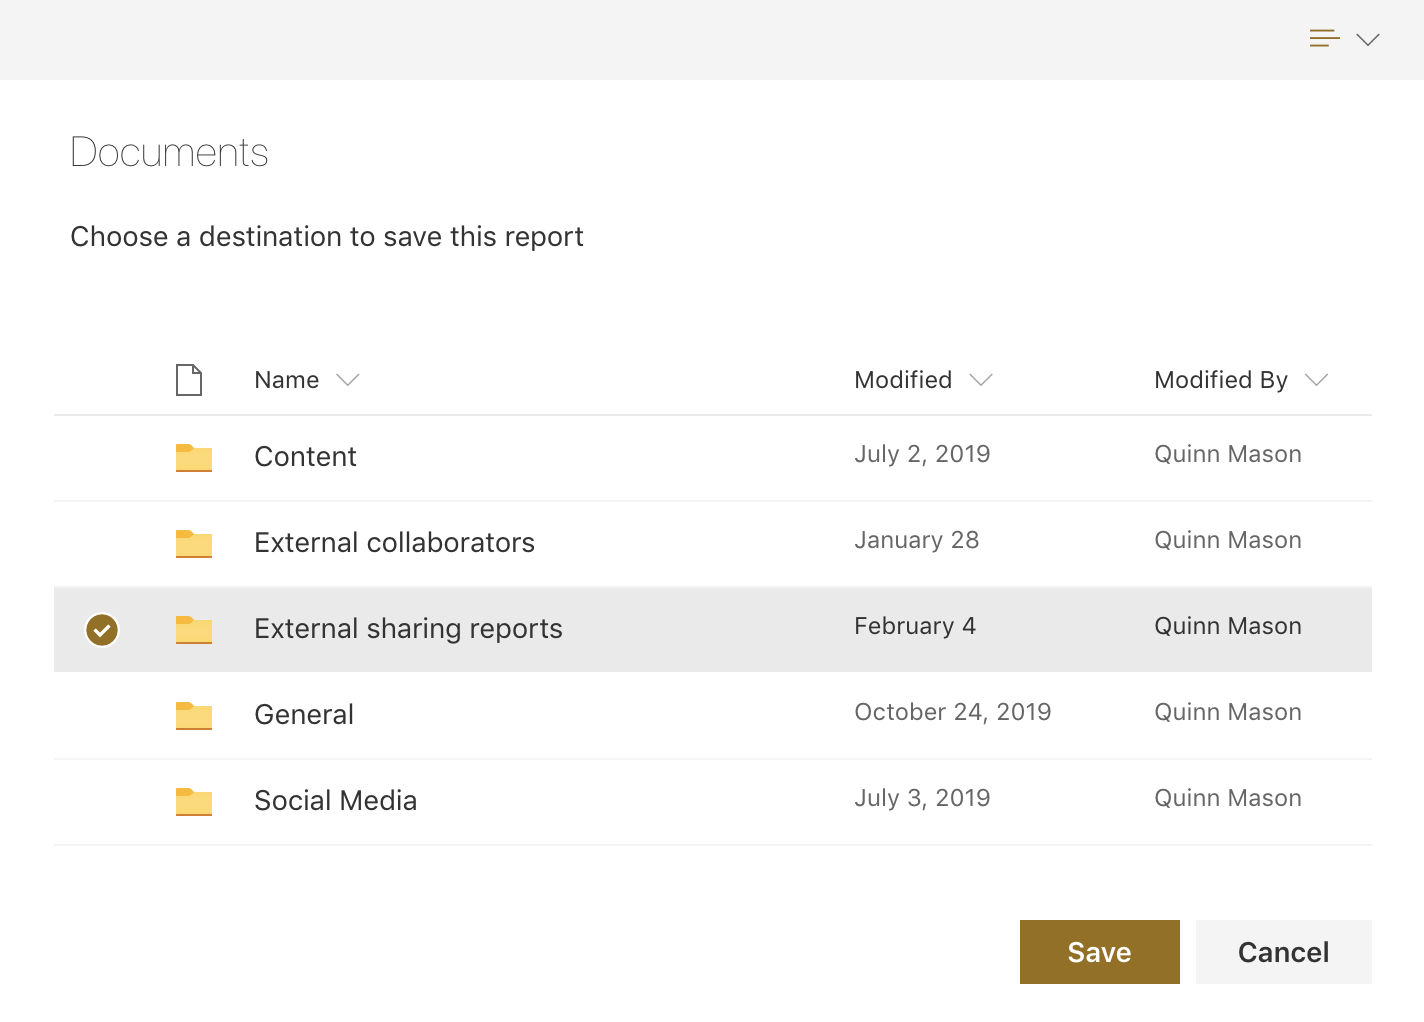
When the report is finished, it will appear in the location you chose on that SharePoint site.
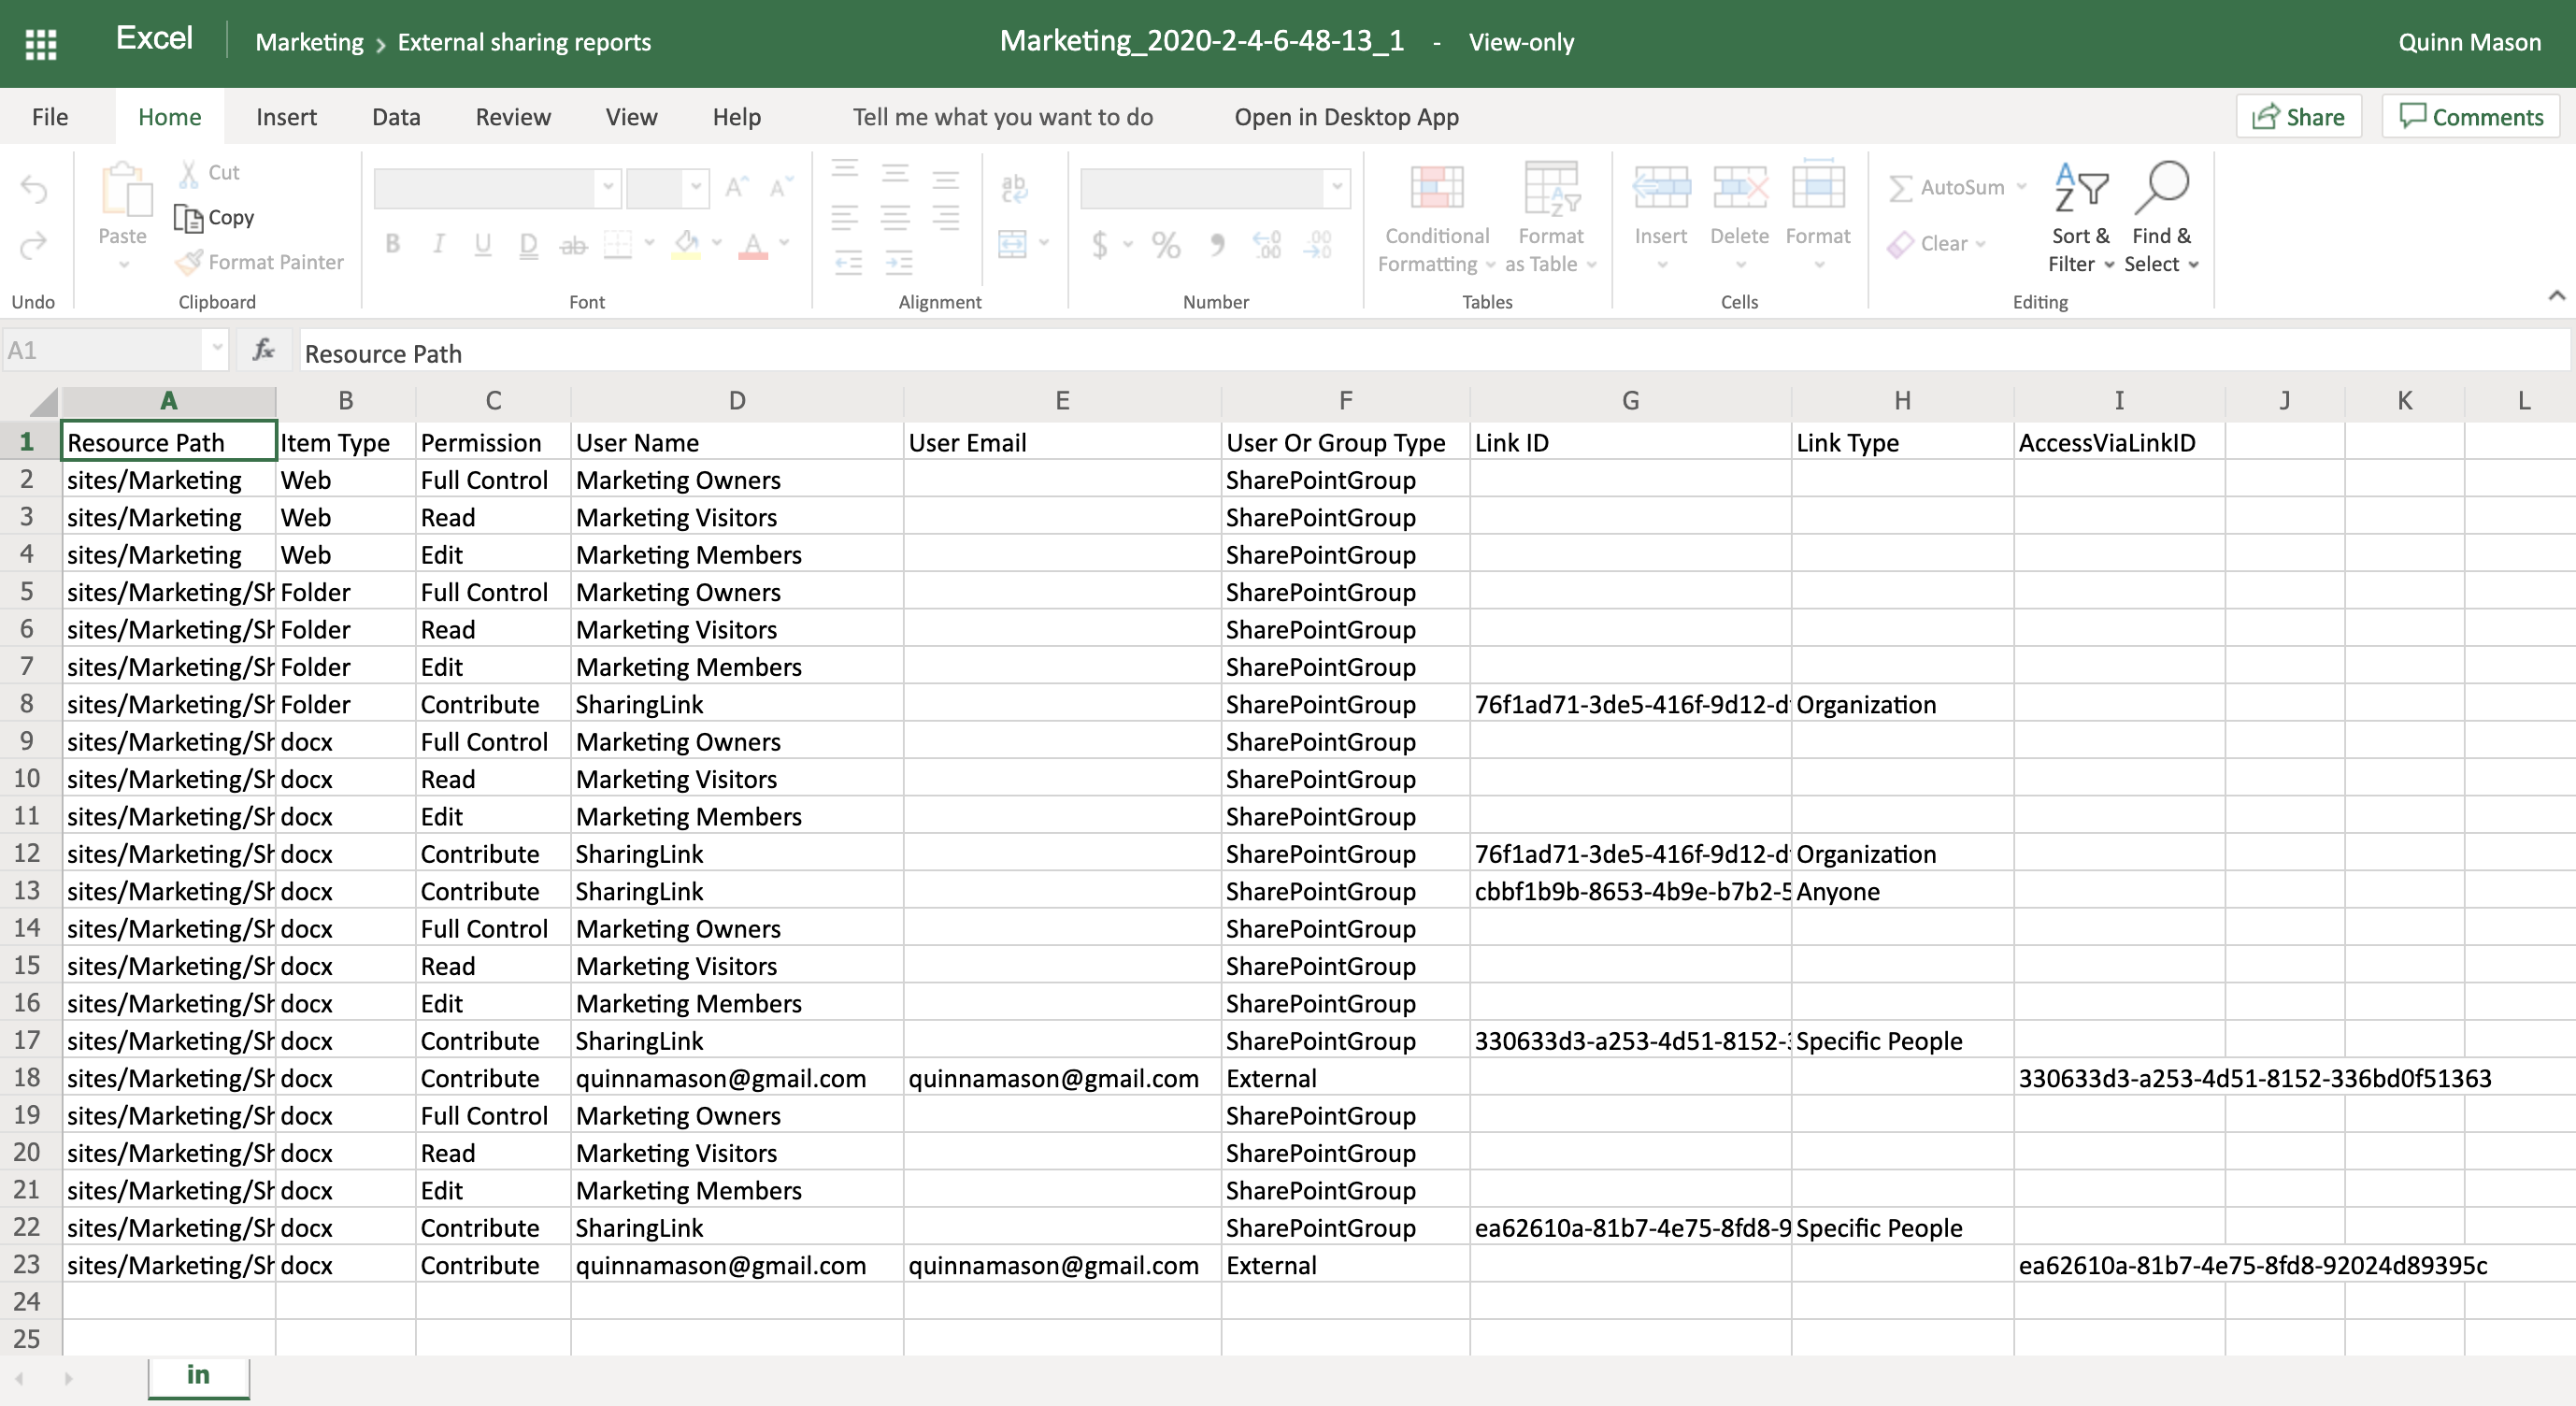
Save it somewhere your site members can’t read it.
The CSV saves onto the site itself, which means by default the people whose sharing you’re auditing can open the audit. Microsoft’s own advice is this:
“If you don’t want site members to see the report, consider creating a folder with different permissions where only site owners can access the report.”
Do this before you run it, not after.
You need to be a site admin on that specific site (not a site member and not a Teams admin). That’s also the reason this doesn’t scale to a whole tenant.
Let’s not forget about the OneDrive version. From the app launcher, open OneDrive > Settings > OneDrive settings > More settings > Run sharing report. Same output, and worth running for anyone who shares heavily from their own OneDrive.
Running this site by site is fine when you’re investigating one team. It falls apart as a routine process, and it used to be the only option. It isn’t anymore. Microsoft now has a tenant-wide version, which is Option #3 below.
Validate external sharing links, and revoke access as needed
Once you've run reports for every team's SharePoint site, you still need to:
- Send each team's report to the owner(s) to validate, then follow up with them to track their progress.
- If they determine that changes need to be made to a sharing link (or access should be revoked), you have to go in SharePoint and do it one file or folder at a time.
You can find more details on how to stop sharing a file or folder in our blog post on the subject. - Then, just like option #1, you have to manually log any changes for compliance and internal auditing reasons.
- Repeat the entire process over again.
With all the manual labor involved, this option is probably even more time-consuming than the first one. And by the time you make it through one review, get ready to start the whole convoluted process over.
To keep your data secure and ensure external users have access to the right things, you need to repeat this process on an ongoing basis.
Option #3: Schedule automatic external sharing reviews
The SharePoint admin center now has tenant-wide reporting under Reports > Data access governance. This is the answer to “I don’t want to run a report on 400 sites.”
Activity reports cover the last 28 days: sites where the most “Anyone” links were created, “People in the organization” links, and “Specific people” links shared externally—that last one being the place to start for our purposes here.
Snapshot reports are point-in-time. The most useful is site permissions across your organization, which has the columns you want when you’re auditing external access:
- ExternalSharing: Whether content on that site can be shared externally at all.
- Guest user permissions: How many permissions are held by guests, at any scope.
- External participant permissions: Microsoft’s definition: “external users who can directly use their own credentials to sign-in and collaborate, such as in Shared channels.” This is your shared channel visibility.
- Anyone link count and People In Your Org link count
- Site Template: so you can filter to team sites.
- Site Sensitivity.
- Items with unique permissions count.
You can download it as CSV and work through up to a million sites offline. Microsoft’s suggested frequency is snapshots quarterly, activity reports monthly.
SharePoint Advanced Management is not included in Microsoft 365 E5. You need a base subscription plus at least one of: a single Microsoft Copilot licence assigned to anyone in the tenant, a SharePoint Advanced Management Plan 1 add-on, or Microsoft 365 E7. On E5 alone you get a cut-down version, and Microsoft spells out what’s missing: “The reports don’t provide snapshot reports or remedial actions. Activity reports are available but can return only up to 10,000 sites.” You also have to enable data collection manually first, it only keeps 28 days, and it pauses after three months if you don’t run anything.

Option #4: Ask site owners to clean up, and track whether they did
Site access reviews are Microsoft’s answer to the exact problem this article describes. You can see the oversharing, but you’re not the person who knows whether it’s justified.
Microsoft frames it the same way we did:
“Site access reviews in the SharePoint admin center enable IT administrators to delegate the process of reviewing data access governance reports to site owners of overshared sites. Compliance reasons prevent IT administrators from accessing file-level or item-level details. Site owners are best positioned to review and address oversharing issues for their own sites.”

From a data access governance report, select the sites you care about and choose Initiate site access review.
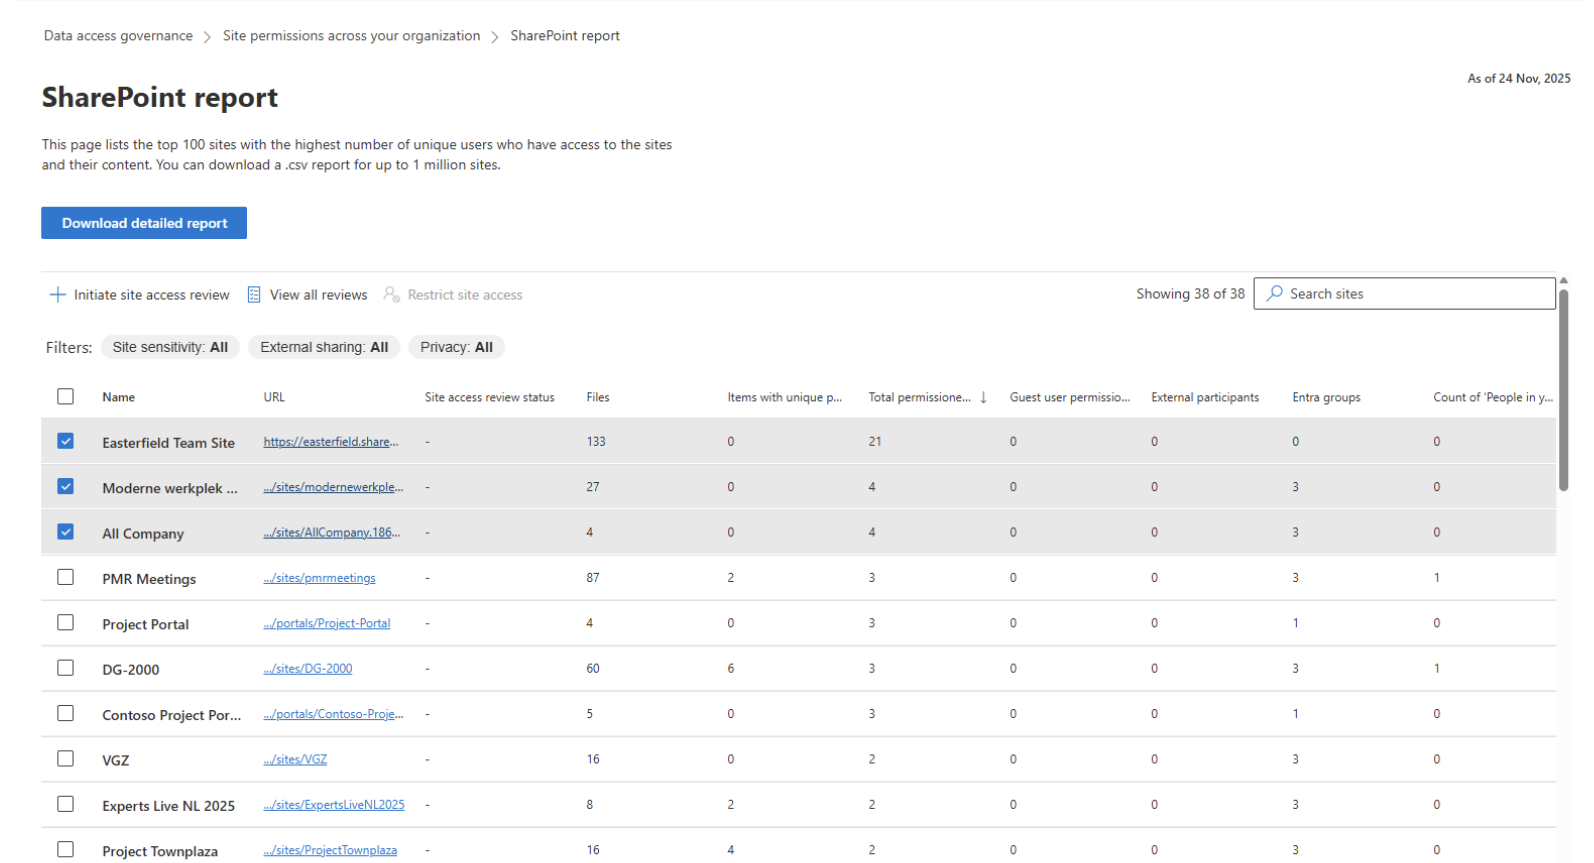
You can customize and preview the email before it goes. Owners land on a review page with a Manage access button, remove or modify permissions, add comments, and select Complete review. This sends their comments back to you. Everything you’ve sent sits under the My review requests tab.
The current limits are:
- Up to 100 sites at a time from the web view, and beyond that you have to use PowerShell (Start-SPOSiteReview).
- Up to 1,000 reviews per calendar month from the site permissions report, resetting monthly.
- SharePoint sites only because OneDrive isn’t supported.
- Not available in Microsoft 365 operated by 21Vianet. Same licensing as Option #3.
Option #5: Review every guest in every team, on a schedule
Microsoft Entra access reviews let you run recurring guest access reviews across your whole tenant and delegate them to team owners.
Set the review scope
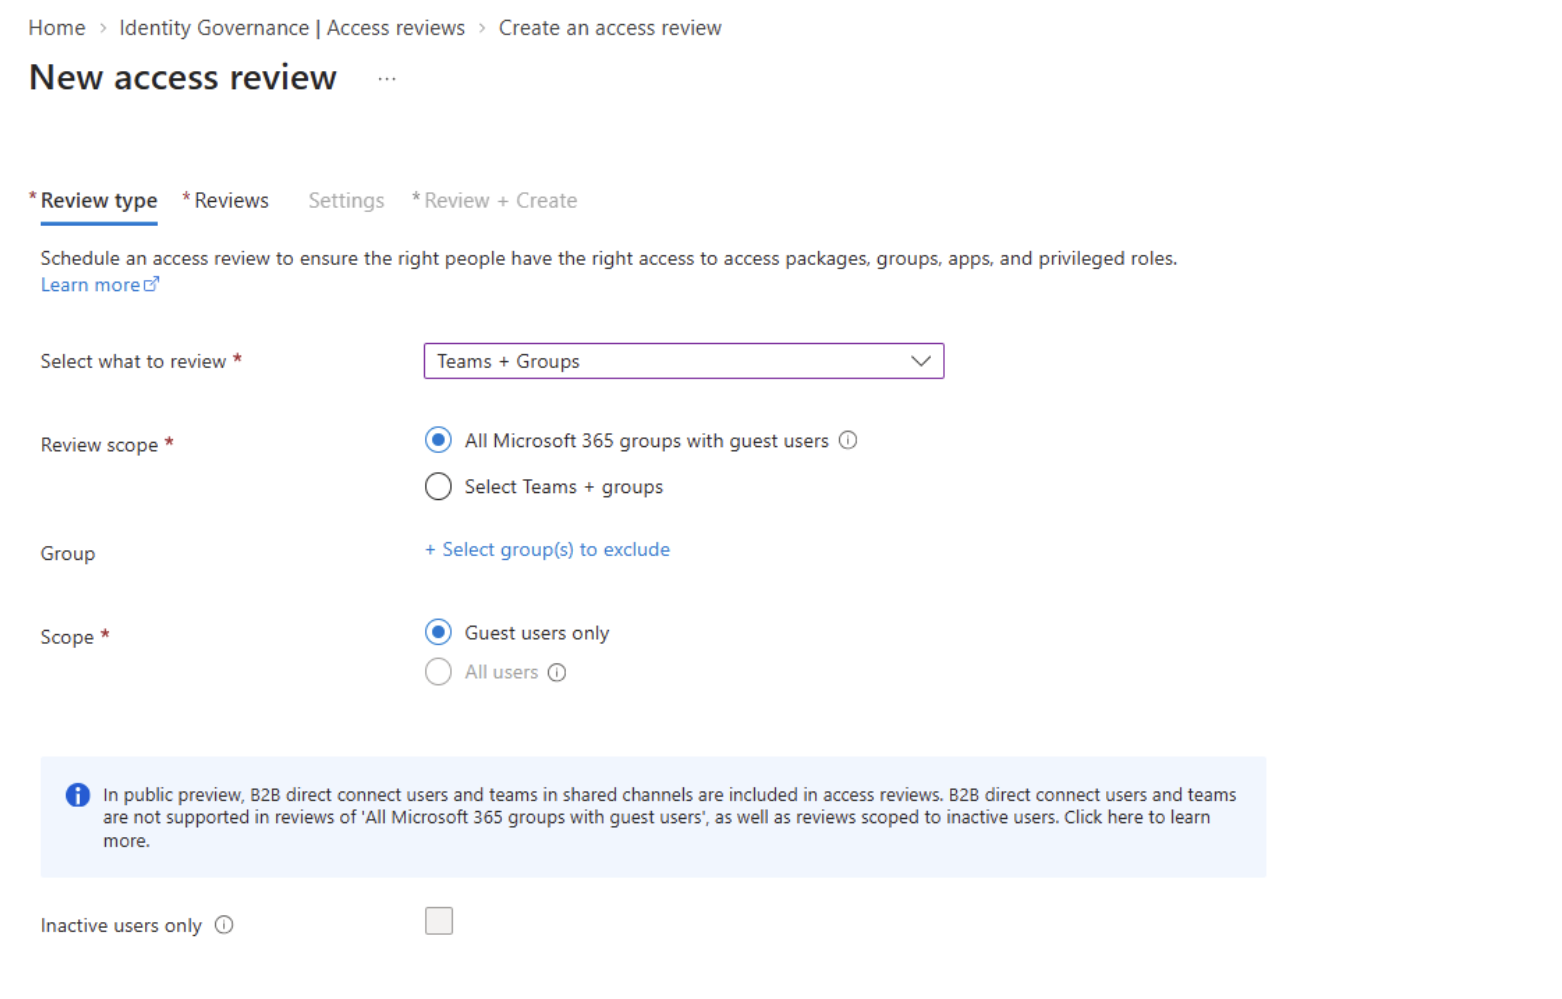
In the review wizard, under Teams + Groups, you get two choices:
- All Microsoft 365 groups with guest users recurring, tenant-wide, with the option to exclude specific groups.
- Specific groups that you choose yourself. If you choose the tenant-wide option, the scope is guest users only.
The reviewers
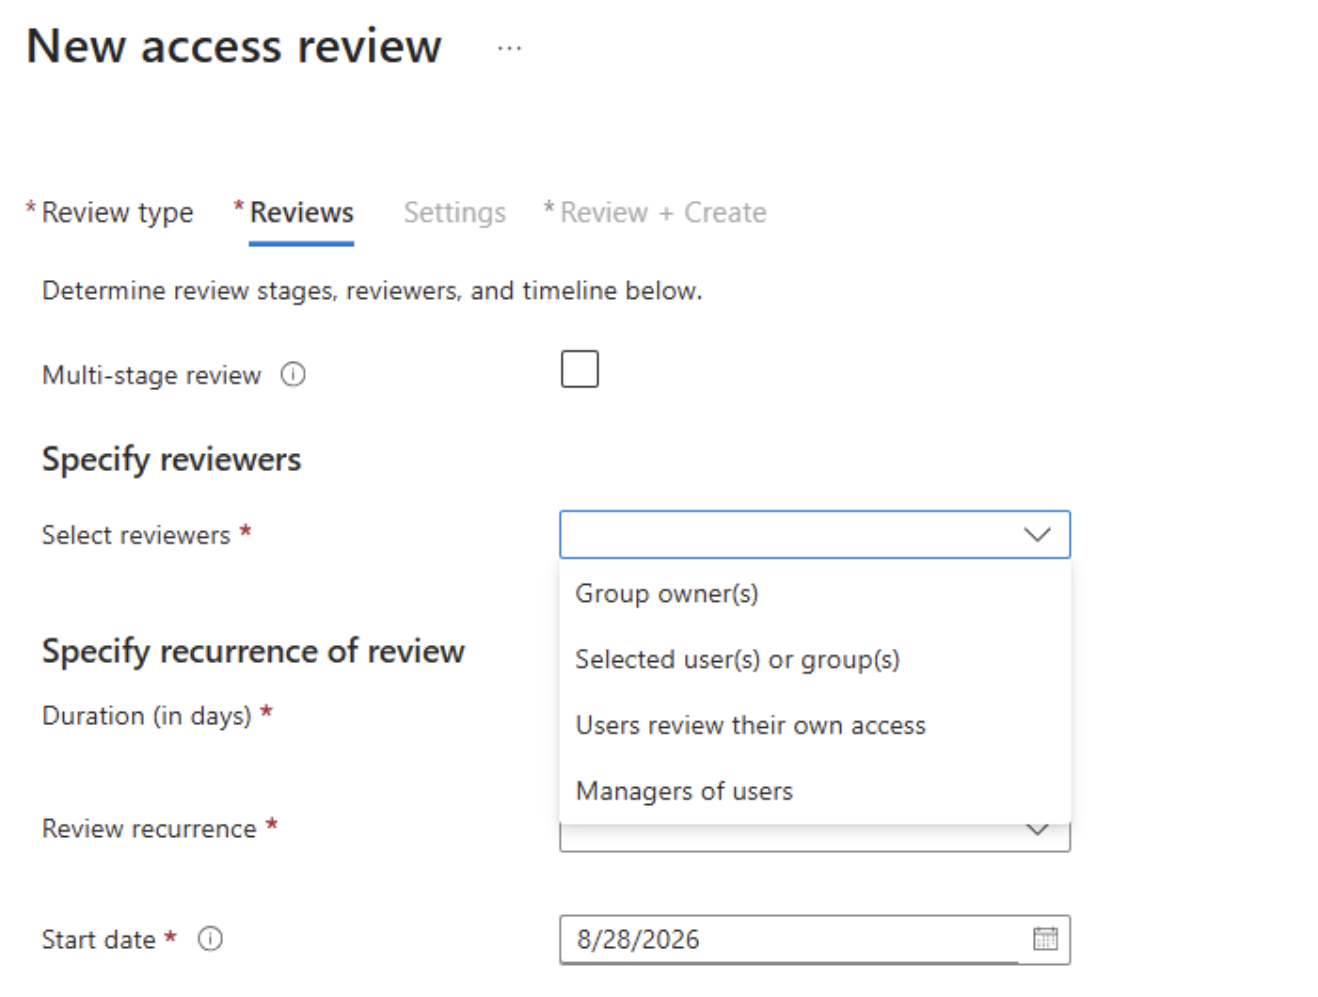
These are the group owner(s), specific users or groups, the users themselves, or their managers. Including a fallback reviewer for any group that has no owner. Multi-stage reviews let guests self-attest first and the owner adjudicate second.
What happens when they don’t respond?
This is the part that takes care of the follow-up work. Set Auto apply results to resource, then choose what happens if reviewers don’t respond: no change, remove access, approve access, or take the system’s recommendation.
For denied guests specifically, you can remove their membership, or “Block user from signing-in for 30 days, then remove user from the tenant.” Reviewers get reminders halfway through the review window automatically.
Microsoft gives one warning that';s worth repeating: if you set “if reviewers don’t respond” to remove access and turn on auto-apply, “all access to this resource could potentially be revoked if the reviewers fail to respond.” Start with a setting that does not remove access until you understand how reliably owners complete their reviews.
You can also delegate the reviews themselves. Under ID Governance > Access Reviews > Settings, let group owners create and manage reviews for their own groups. It’s off by default.
For the stale ones, Entra ID Governance has an inactive guest report (ID Governance > Dashboard > Guest access governance > View inactive guests) with a configurable threshold defaulting to 90 days, exportable for up to a million guests. Reviews can be scoped to inactive users with a Days inactive value up to 730 days, and recently created guests are automatically excluded so you don’t immediately delete someone you invited last week.
What will it cost you?
Guest access reviews of teams and groups, owner-delegated, recurring, with auto-apply and block-and-delete, run on Microsoft Entra ID P2. You already have this with Microsoft 365 E5.
Reviews scoped to inactive users, the inactive guest dashboard and machine-learning recommendations need Microsoft Entra ID Governance or Entra Suite, not P2. Any governance action against a guest account brings guest monthly-active-user billing: connecting the Entra ID Governance for Guests add-on is enforced from January 2026, and there is no free tier for governance billing.
Learn more about Microsoft Entra ID governance licensing in Microsoft's official documentation.
Option #6: Let Microsoft Purview find the oversharing for you
Data risk assessments in Microsoft Purview DSPM run automatically.
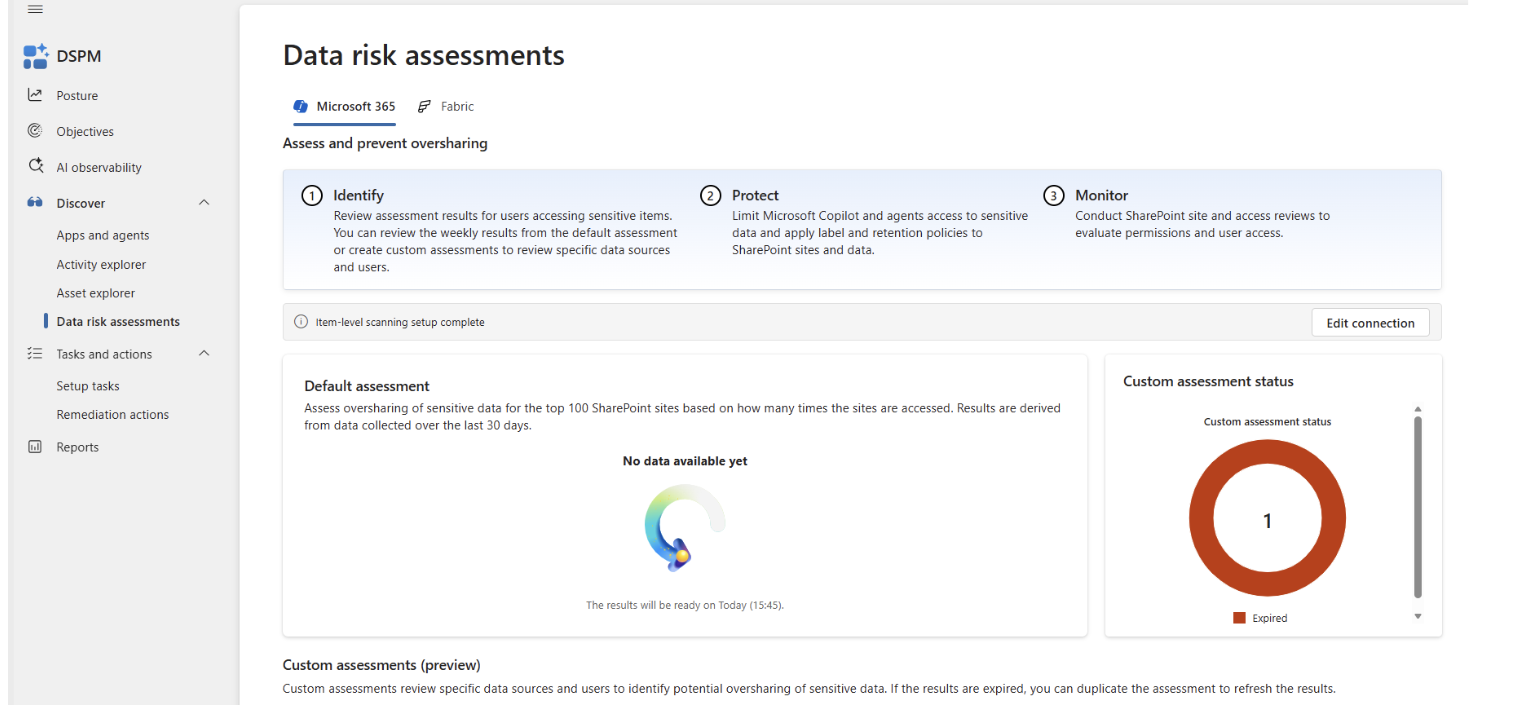
A default assessment covers your top 100 SharePoint sites by usage every week, and the monitor tab breaks down how many items on each site are shared with anyone, with everyone in the organization, with specific people, and externally. Including a button to launch a SharePoint site access review straight from there.
Custom assessments add item-level scanning, which shows items as potentially overshared if they have a sharing link for external or anonymous users, and gives you remediation in place: apply a sensitivity label, notify the site owner, or remove the sharing link.
The limitations:
- Maximum of 200,000 items per location
- Current maximum of 10 SharePoint sites for item-level scanning,
- No OneDrive support for item-level scans
- 48-hour wait for results to settle.
- Requires Microsoft 365 E5 or the Purview Suite.
Better than reviewing: stop the sprawl at the source
The most effective external access review is the one you don’t have to run.
Cross-tenant access settings
Rather than allowing open collaboration with any external organization, define cross-tenant access settings deliberately:
- Configure access rules for each partner organization where you need closer control.
- Use inbound access settings to decide which external users, groups, and applications can access your environment.
- Use outbound access settings to decide which of your users, groups, and applications can access other organizations.
- Decide whether to trust MFA, compliant device, and hybrid joined device claims from partner tenants.
- Use tenant restrictions when you need to control how external accounts are used from your network or managed devices.
Worth knowing the defaults: B2B collaboration with other Microsoft Entra organizations is enabled by default, while B2B direct connect is blocked by default. Cross-tenant access settings let you scope access to specific users, groups, and applications instead of leaving collaboration broadly open.
Sensitivity labels for per-team guest control
Guest access in Teams is an org-wide setting but you can control guest access to individual teams by using sensitivity labels. A label scoped to groups and sites can control whether owners can add guests at all, external sharing from the SharePoint site, access from unmanaged devices, and which teams can be invited into a labelled team’s shared channels.
Group and team expiration
A Microsoft 365 Groups expiration policy deletes unused groups, and since teams are backed by groups, it applies to teams as well.
Auto-renewal triggers on real activity such as viewing or editing a file in SharePoint, visiting a Teams channel. Notifications go out at 30 days, 15 days and 1 day before expiry, and a deleted group is restorable for 30 days. You only get one expiration policy per tenant, and it requires Entra ID P1 or P2 licences to be held, though not necessarily assigned, for affected members.
Often the fastest way to remove external access to a team is to remove the team.
How to run Delegated Reviews in ShareGate
One admin can't be the decision-maker across hundreds or thousands of workspaces. The person who knows whether a guest still needs access is usually the person working with them. These aren't questions IT can answer on behalf of business users.
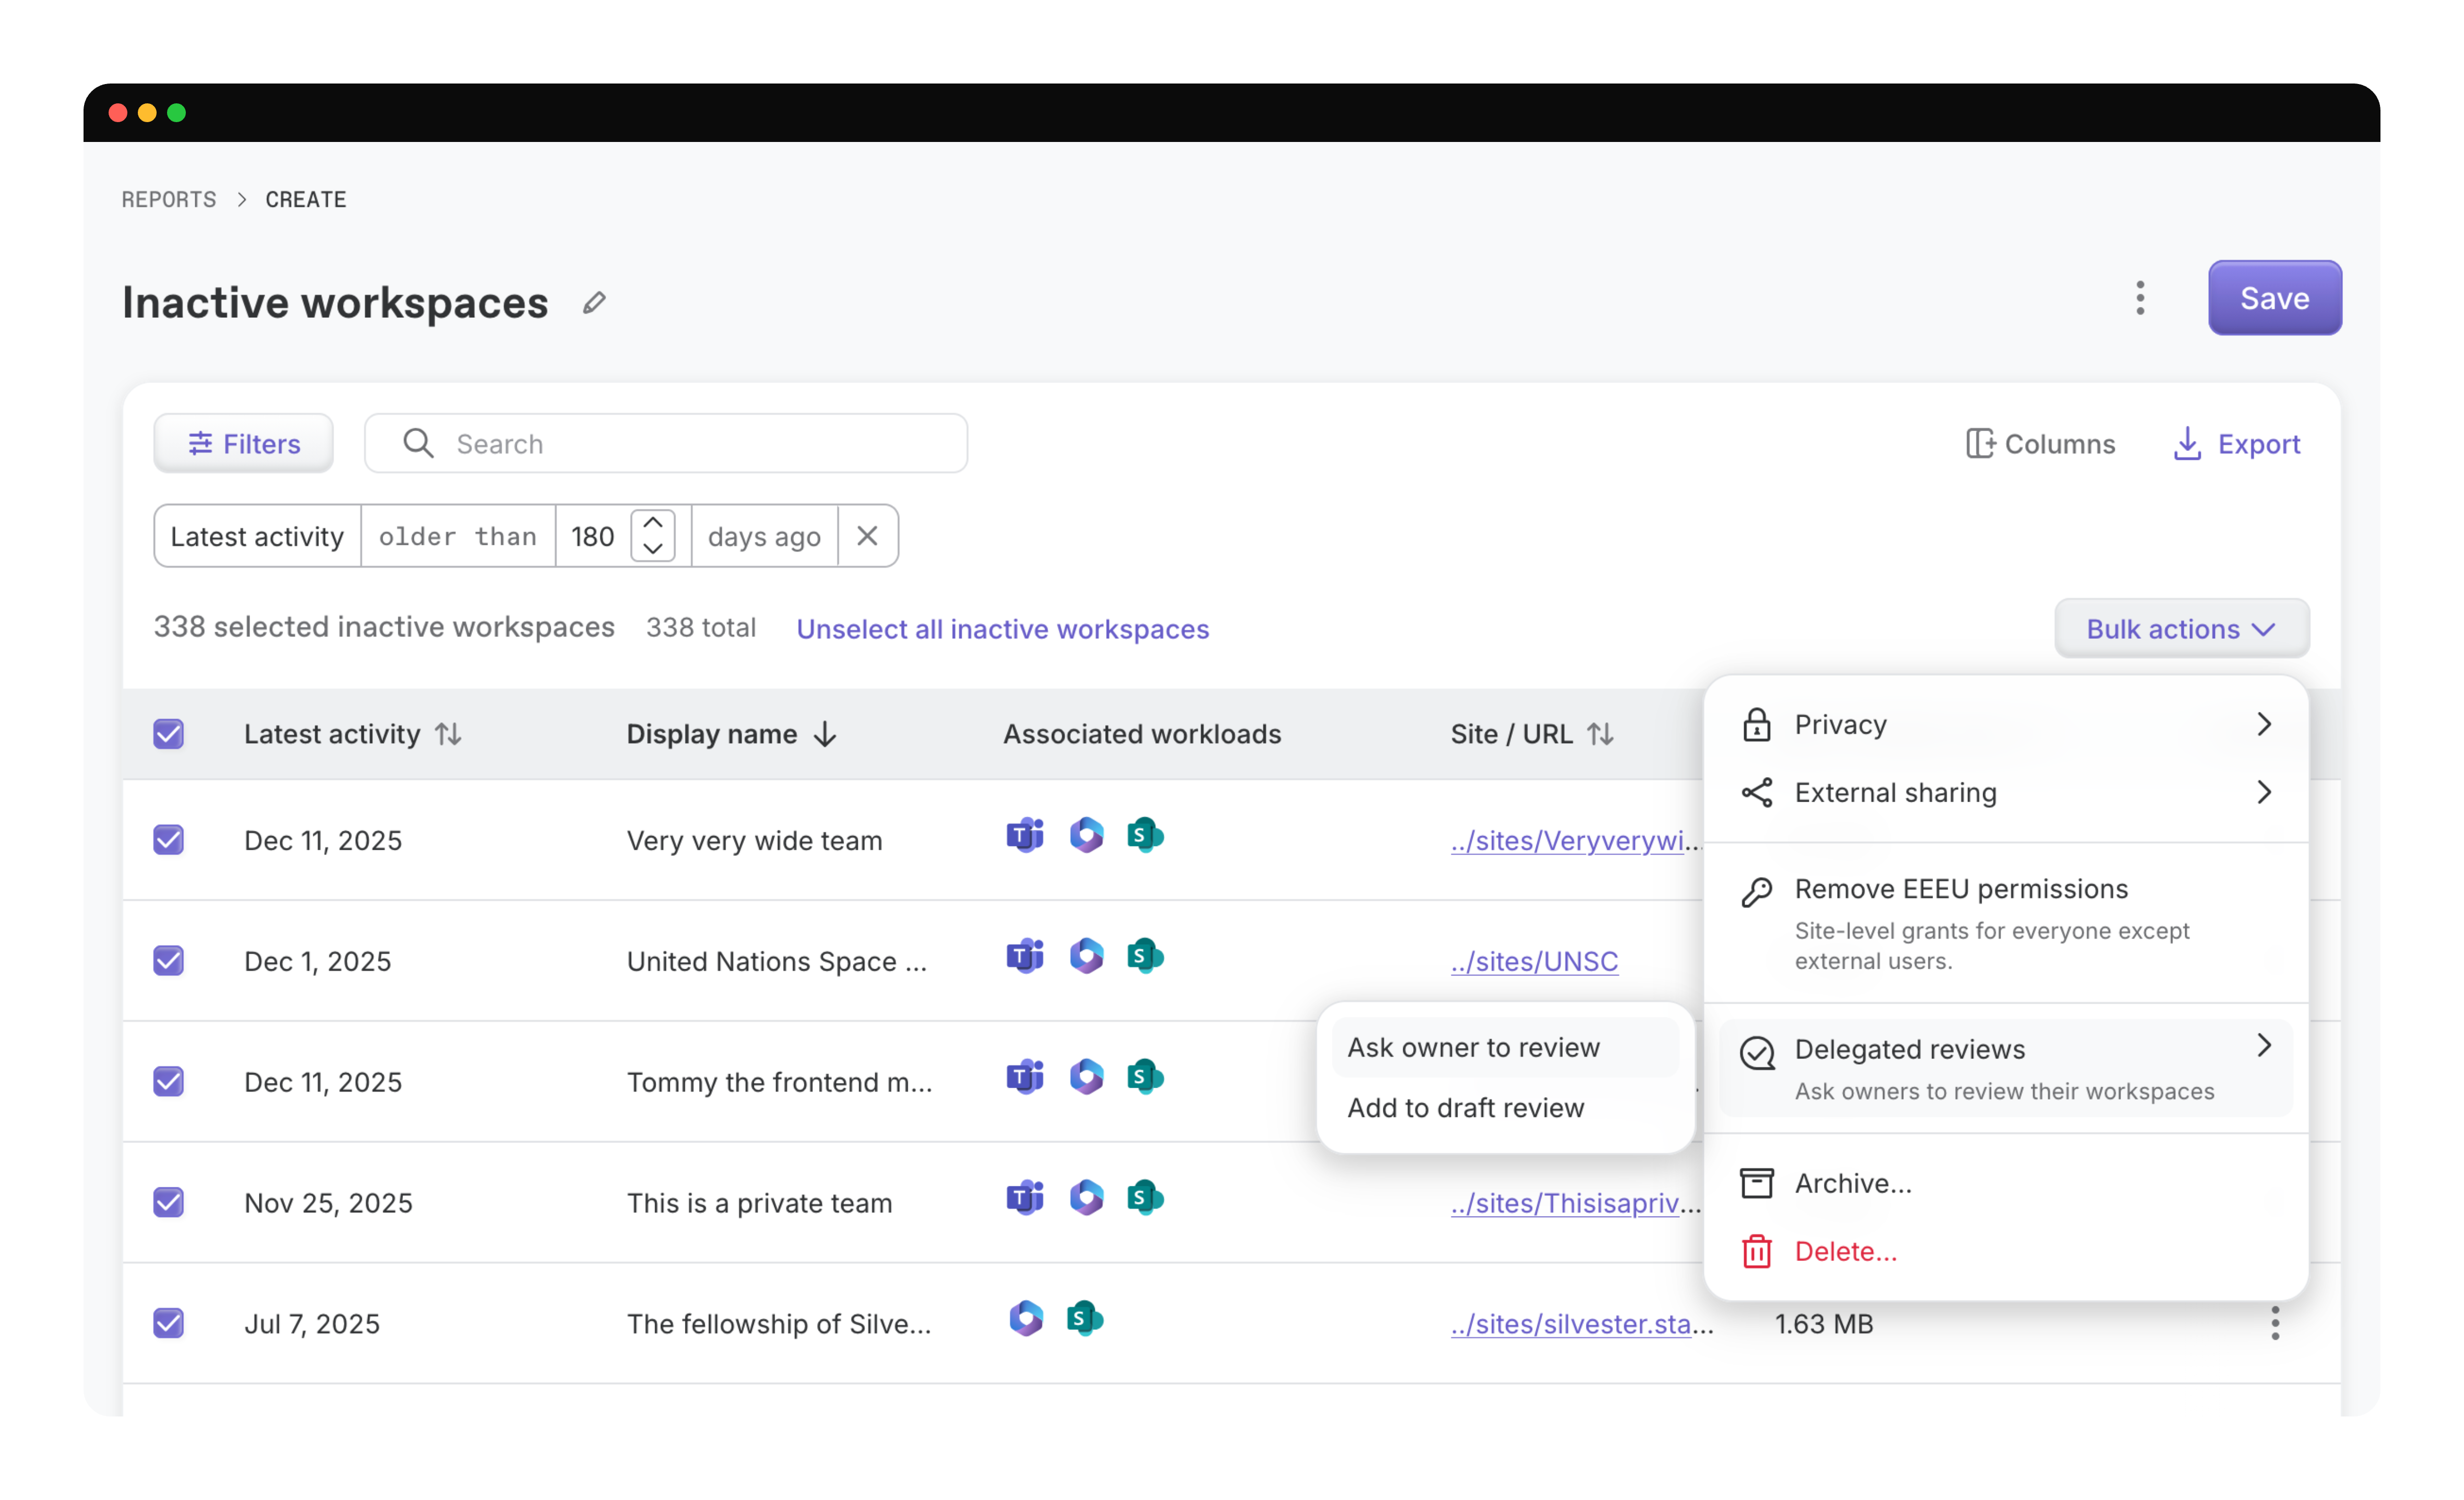
Delegated Reviews puts the decision where the context lives.
Select workspaces from any Protect report covering SharePoint, Teams, or Groups, bundle them into a review, and send it to the owners. They get a link, sign in with their Microsoft 365 account— no ShareGate account needed—and decide whether to keep, archive, or delete a workspace, remove a guest, or kill a stale sharing link. Actions run the moment they submit.
This is what it looks like for the business user:

You stay in control of what gets reviewed and by when
You choose the workspaces, set the deadline, and dispatch. From the Reviews page, you can track exactly who's responded and who hasn't—and nudge anyone dragging their feet.
Every decision builds a governance trail
Every action lands in the Activity Log with who made it and why. You're not just distributing the work—you're building a record the whole organization can stand behind.
Learn more about Delegated Reviews in ShareGate
Related Microsoft 365 documentation:
Report on externally shared files and folders in a SharePoint site


Don’t just migrate it, ShareGate it.
Your source is never touched — ShareGate only copies.
Re-running is safe, included, and free.